The Agentic Cybersecurity Engineering Platform
One ACE Platform to hunt, detect, investigate, and triage activity before it becomes an incident.
Trusted by




Agentic Cybersecurity Engineering
The Nebulock ACE Platform
Unify threat hunting, detection engineering, insider risk, and alert triage on a single architecture. Powered by the TRACE Graph’s contextual memory, the ACE Platform makes security teams more proactive against human and agentic threats.
TRACE GRAPH
Memory that compounds across every workflow
Most security tooling reasons about your environment one alert at a time, then throws it away.
The TRACE Graph is Nebulock’s behavioral system of record. It holds your entities, telemetry, rules and policies, signals, findings, and every hunt you have run. The knowledge compounds, not resets, when a case closes.
That memory is why the ACE Platform is not limited to hunting. We baseline what normal looks like, and apply that context to detections, insider risk, and alert triage for better evidence-backed outcomes.
VESPYR
YOUR AGENTIC HUNTER
Vespyr hunts without a directive, turning a threat intel report into a deployable detection in minutes.
It shifts your workflow from agentic to fully autonomous. Rather than needing human prompting to initiate, Vespyr monitors intelligence sources, determines relevance, and delivers findings.
The human can then review, validate and act. The agent does everything before that - allowing you to unlock continuous, threat-informed defense.
HELIX
Just-in-time DATA enrichment
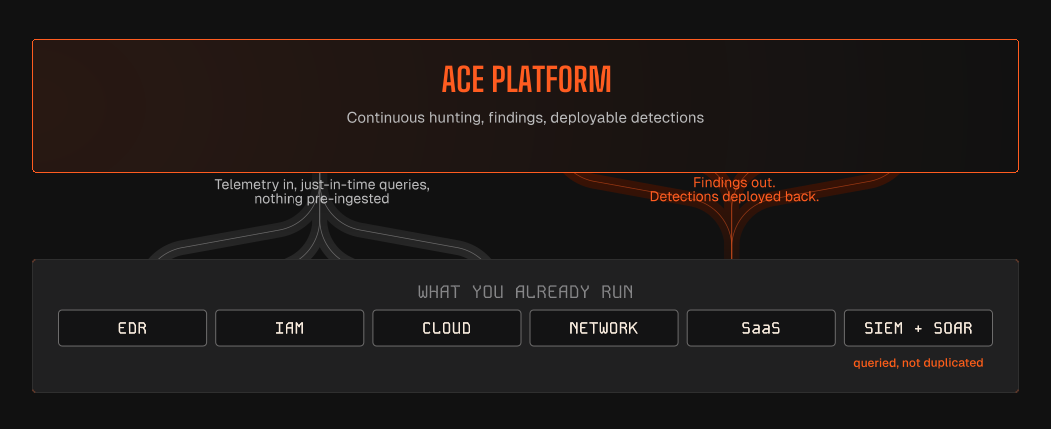
Query the tools you already run at the moment a hunt, investigation, or detection needs them, with nothing pre-ingested.
Helix connects to your security tools with federated search to get data just-in-time, not just-in-case. This means you can query and reason over data from tools like vulnerability management, without ingesting, indexing or storing.
Helix queries the authoritative system only when relevant, and carries the relevant information into the finding.
Alert triage
Close alert noise at the source
Alert triage that starts with context instead of rebuilding it for every alert.
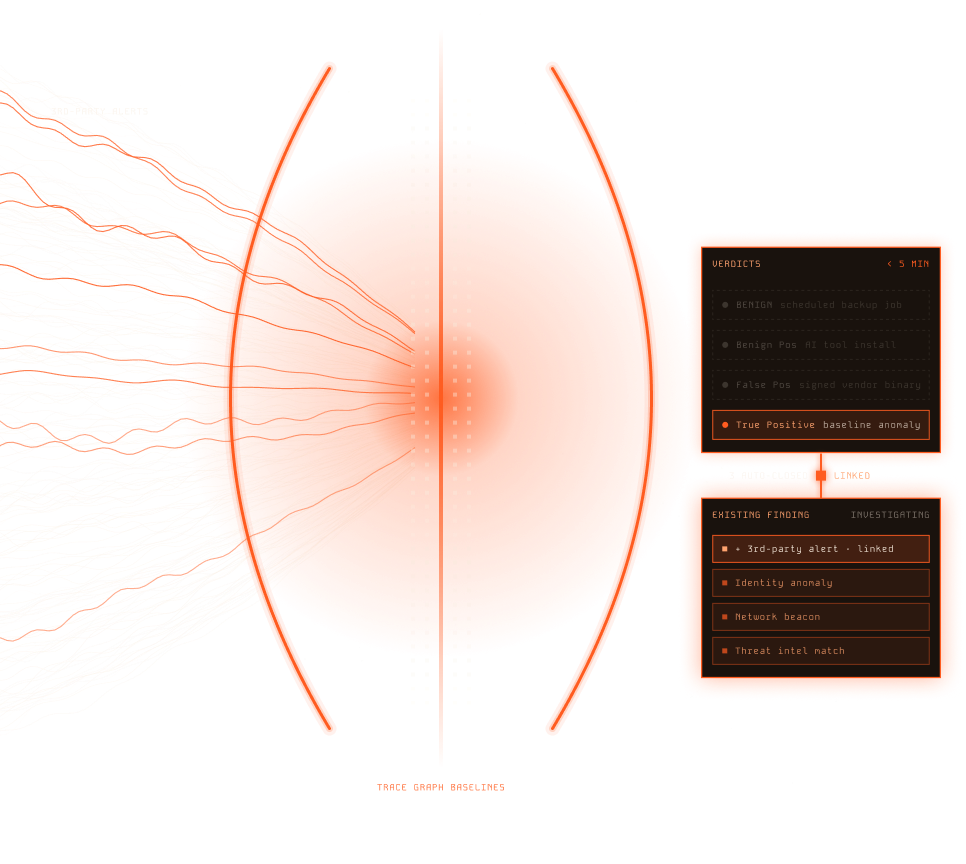
Nebulock triages alerts from your third-party security tools against TRACE Graph baselines and returns a verdict with its reasoning in under five minutes. True positives are linked to existing findings in TRACE Graph for investigation. Benign and false positives can be auto-closed, so analysts never have to work them. You keep your tools and your workflow. We change what reaches the queue.
command center
Centralize your security operations
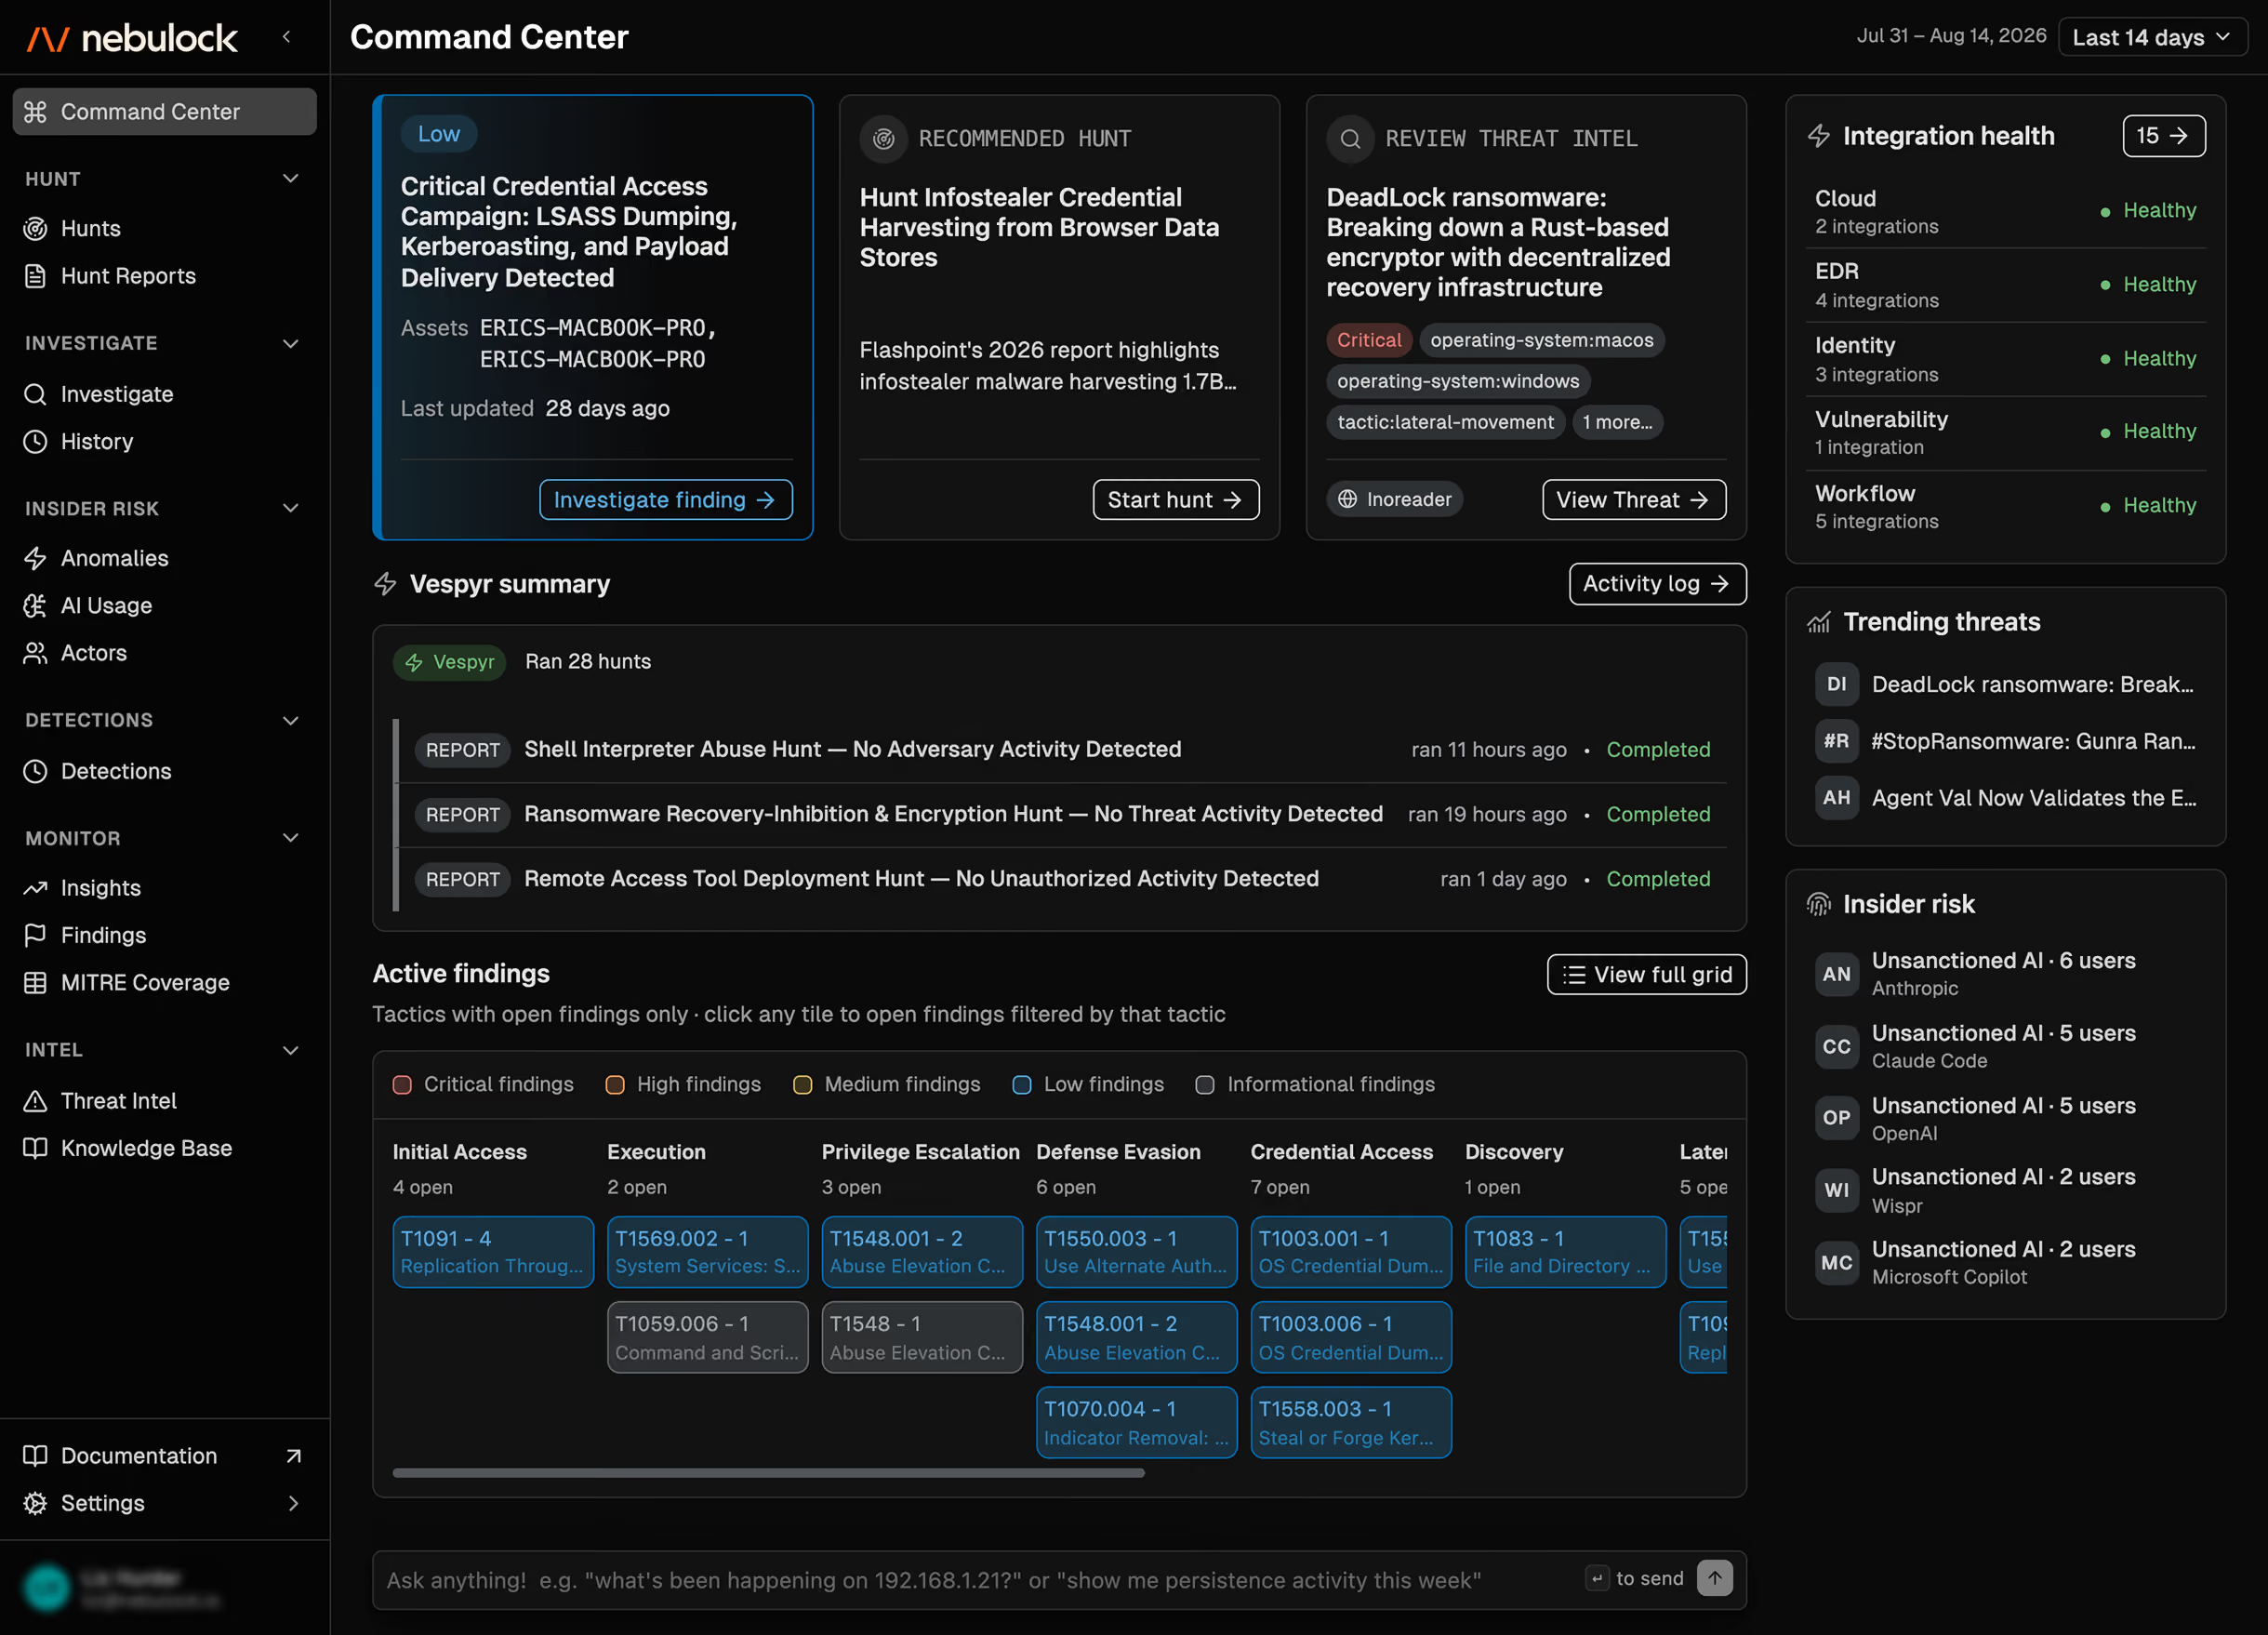
Command Center is the home base your team opens first.
At the top, you’ll see your most critical finding, the hunt we recommend you run, and the intel worth acting on. You can start a hunt or investigation, see what Vespyr hunted autonomously, insider risk threats, and more.
No pivoting between six consoles to build the picture in your head before you can start working.
What you get
From every hunt


Calibrated findings
Know what to act on before you spend cycles. Nebulock labels every finding with evidence-based confidence levels, so analysts can quickly act, escalate, or close. No black-box risk scores.

Reports your CISO can read
Turn a hunt into a decision, not a write-up. Every hunt closes with hypothesis, evidence, MITRE mapping, and recommendations. Hand it to the board or an auditor without rewriting a line.

Investigations you can reopen
Your hunts get smarter and don’t expire. Case-centric tools forget the moment the case closes. Nebulock's context compounds, so even with new intel every hunt makes investigations faster.
INTEGRATION
Part of your security stack
Nebulock’s ACE Platform sits on top of what you already run. Findings and detections deploy into your SOC workflows, and telemetry from your EDR and SIEM are used for hunts and investigations.
HUNT-DRIVEN DETECTIONS
FROM INTEL TO DETECTION IN MINUTES
Operationalize your CrowdStrike, Mandiant, community intel feeds, and even blogs/news articles. Nebulock hunts off any intel across your environment, determines if you're affected, and automatically creates a durable detection rule to deploy to protect your environment today or in the future.


Detections that earn their place
Grow your coverage without detection drift. Run Retrohunts on detection logic back through your past telemetry to validate and test rules for efficacy. With the TRACE Graph as the memory, see how it performs deploying it in production. Fewer tuning loops, fewer false positives in the queue, and more of your team's time on real threats.
SEE Nebulock
in action
Explore Nebulock’s Agentic Cybersecurity Engineering Platform.